Prove control before audit time.
Compliance is preventive security, not a standalone GRC exercise. Policy is enforced before a fix ships, checked again in live infrastructure, and turned into a signed audit pack auditors can use.
ops0 brings your clouds, runtime, infrastructure code, and workflows into one operating context. Continuous compliance enforces policy checks before deployment and scans live infrastructure afterward, producing audit evidence across six frameworks: SOC 2 Type II, CIS, ISO 27001, ISO 27002, HIPAA, and GDPR, shared as snapshot reports or signed audit packs for a chosen audit period.
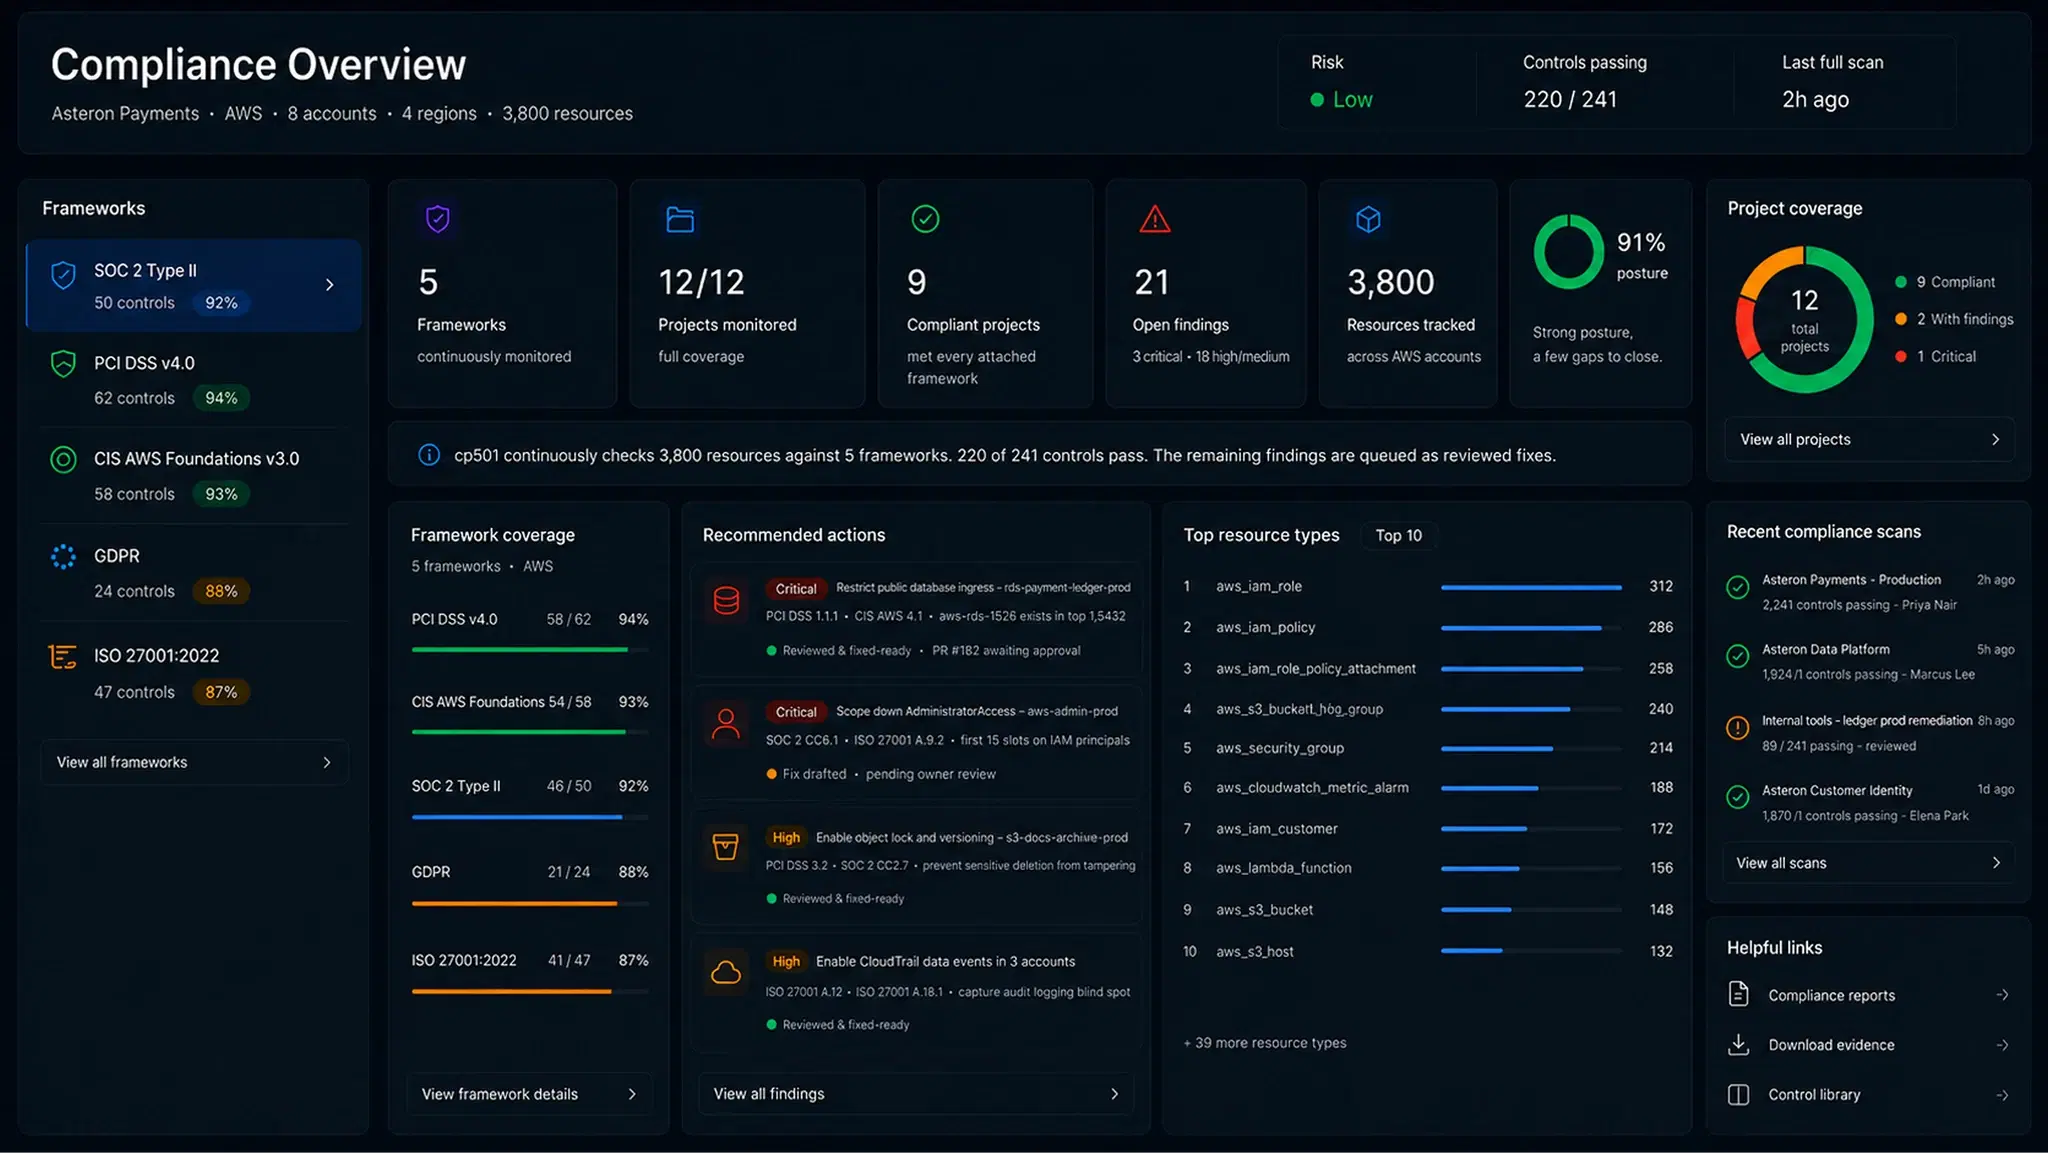
Audit season is a scramble for evidence. Here the evidence is already there.
Checked before it ships.
137 policies run against the plan. One fails: a storage bucket without encryption.
Compliance that runs, not a checklist.
Policy, before and after deploy.
One policy engine, every framework.
One policy engine, checked against SOC 2 Type II, CIS, ISO 27001, ISO 27002, HIPAA, and GDPR at the same time.
One fix closes both frameworks at once.
ops0 itself is SOC 2 Type II.
Common questions
Make compliance
continuous, not ceremonial.
Evidence should already exist before the auditor asks. ops0 keeps policy results, live findings, and deployment records together, ready to share as a signed audit pack.