Infrastructure as code

Turn live cloud into reviewed code.

Codify discovered state or plain-language intent into Terraform, OpenTofu, or Oxid, with the guardrails you already run present from the start.

Terraform, OpenTofu, and Oxid
Policy checks before generation
Cost estimated before apply
Secrets never shown to the AI

ops0 brings your clouds, runtime, infrastructure code, and workflows into one operating context. Reviewed IaC turns a discovered finding or a plain-language request into policy-aware Terraform, OpenTofu, or Oxid, ready for approval before it becomes an incident.
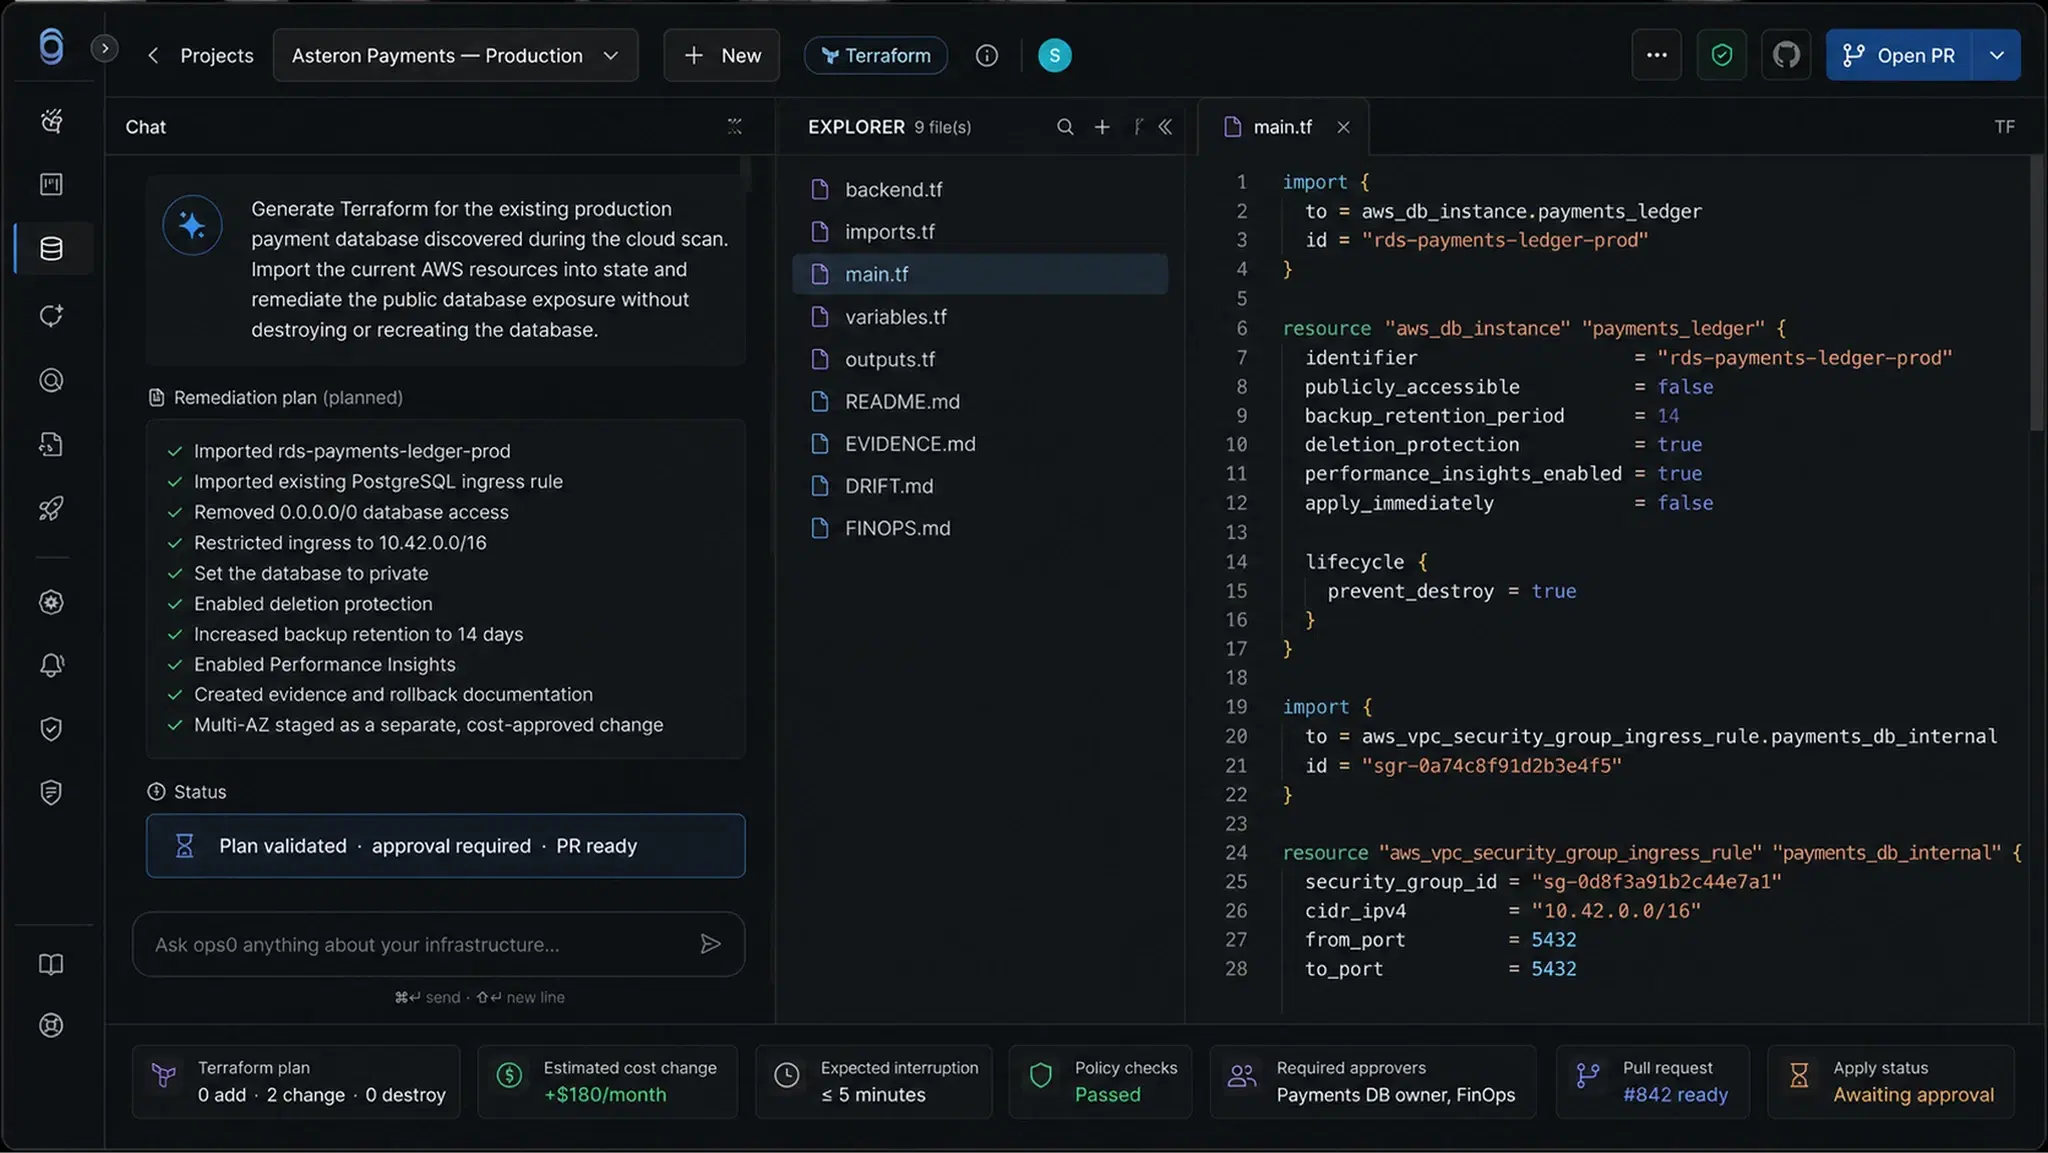
ops0.ai/features/iac/generate
ops0 reviewed IaC: generated Terraform for a discovered finding, policy checks passed, cost estimate, and approval status

Writing Terraform for what already runs is busywork. ops0 reads the resource and writes the code. 

TerraformOpenTofuOxidImport, not recreate
Live cloud to code
01 / 04 · Pick

Start from what is running.

rds-payments-ledger-prod exists in AWS, but in no Terraform file.

LIVE RESOURCEGENERATED CODErds-payments-ledger-prodAWS · RDS · us-east-1NO TERRAFORM FILEenginepostgres 15.4instance_classdb.r6g.largeallocated_storage500storage_encryptedtruepublicly_accessibletruebackup_retention_period14vpc_security_groupssg-payments-db-admin-prodimport {to = aws_db_instance.payments_ledgerid = "rds-payments-ledger-prod"}resource "aws_db_instance" "payments_ledger" {engine="postgres 15.4"instance_class="db.r6g.large"allocated_storage=500storage_encrypted=truepublicly_accessible=truebackup_retention_period=14vpc_security_group_ids= "sg-payments-db-admin-prod"}Plan: 1 to import, 0 to add, 0 to change, 0 to destroy.PR #842
Going deeper

Code you would have written yourself.

From reality to code

Codify what is already running.

Codify from discovered state, or describe what you need to Kiwi.
Terraform, OpenTofu, or Oxid, your choice per project.
main.tfGenerated
import {
  to = aws_db_instance.payments_ledger
  id = "rds-payments-ledger-prod"
}

resource "aws_db_instance" "payments_ledger" {
  publicly_accessible     = false
  deletion_protection     = true
  backup_retention_period = 14

  lifecycle { prevent_destroy = true }
}
TerraformOpenTofuOxid
Under the hood

Built for the code you already have.

Four engines
Write it the way your repo already reads.
resource "aws_db_instance" "payments_ledger" {
  engine = "postgres"
TerraformOpenTofuOxidCloudFormation

One project, one engine of your choice. Generation matches what your repo already uses.

Checked on every line
Findings land on the exact line.
terraform validatepassed
publicly_accessible = trueTFLint
deletion_protectionCheckov CKV_AWS_16

terraform validate, TFLint, and Checkov run on the generated code before it reaches you.

Kiwi asks first
A missing decision stops the write.
provider? auth? public?
Kiwi asks before it writes, not after.
Bring your repo
Connect the repository you already have.
Repositoryops0-ai/payments-infra
Branchmain, PR per change
Folderenvs/prod/rds

Generated code lands in your branch and folder, and stays in sync as the repo changes.

Share a module safely
A redacted snapshot, not repo access.
Snapshot link
ops0.ai/s/8f2c···
password · ••••••expires in 7d
Secrets stay out
Never in the code, never sent to the AI.
InjectedAt apply, as TF_VAR
Shown to AINever
AWS Secrets ManagerGCP Secret ManagerAzure Key VaultOracle Vault

Common questions

ops0 uses the risk finding, user intent, project context, discovered resources, dependencies, and policy rules to generate reviewable Terraform, OpenTofu, or Oxid code.

Describe it, or discover it.
Ship reviewed code.

Start from live cloud or a plain-language request to Kiwi. Every generated change carries its policy, cost, and approval context.

Explore Deployments